Home›Tags›#vulnerability

Tag timeline

#vulnerability12 total

同じキーワードで束ねられた更新を確認できます。カテゴリをまたいだ関連ニュースや実装トピックの追跡に使えます。

Total12#vulnerability の全掲載記事All listed entries tagged #vulnerability
Showing12このページの件数Entries on this page
Page1/1静的ページ位置Static page position
Updated一覧の更新時刻List last updated

Entriespage 1/1 · 12 total

8/25(火)Tue, Aug 251 entries
公式OfficialEditor·Zed Editor Releases

Zed Editor v1.16.2 リリースZed Editor Releases v1.16.2

重要度 InfoInformational深掘り候補 · 公式リリース · EditorDeep-dive candidate · official release · Editor

AI要約Zed Editor v1.16.2では、拡張機能経由のファイルシステムサンドボックス脱出脆弱性を修正し、GitHub Enterprise Cloud環境でのCopilot Chat認証問題も解消。セキュリティと安定性を重視するチームに恩恵をもたらす。

AI SUMMARYZed v1.16.2 patches a sandbox escape vulnerability in extensions and fixes Copilot Chat auth and API routing for GitHub Enterprise Cloud, benefiting security-conscious teams and enterprise users.

Zed Editor Releases v1.16.2
8/24(月)Mon, Aug 241 entries
公式OfficialEditor·Zed Editor Releases

Zed Editor v1.17.1-pre リリースZed Editor Releases v1.17.1-pre

重要度 InfoInformational深掘り候補 · 公式リリース · EditorDeep-dive candidate · official release · Editor

AI要約Zed Editor v1.17.1-pre は、拡張機能経由のファイルシステムサンドボックス脱出脆弱性を修正し、GitHub Enterprise Cloud 環境での Copilot Chat 認証問題も解消したパッチリリース。旧バージョンの拡張 API を使うプロジェクトでも言語サーバー設定が正しく反映されるようになった。

AI SUMMARYZed v1.17.1-pre patches a filesystem sandbox escape vulnerability in extensions, restores Copilot Chat auth for GitHub Enterprise Cloud users, and ensures project-level language server settings work correctly with older extension API versions.

Zed Editor Releases v1.17.1-pre
8/18(火)Tue, Aug 181 entries
公式OfficialGemini/Gemma·Google Cloud Blog

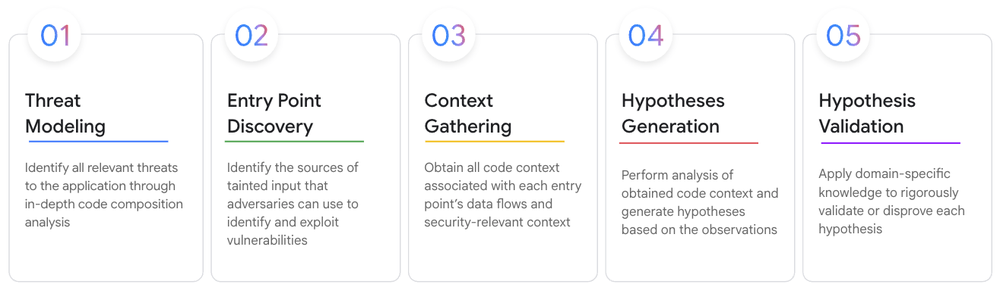
エージェント型ソースコードレビューで敵対的AIの脅威に先手を打つStaying Ahead of Adversarial AI Through Agentic Source Code Review

重要度 MediumMedium priority技術記事 · Gemini / Gemmatechnical post · Gemini / Gemma

AI要約GoogleのMandiantチームが、AIエージェントと人間の専門知識を組み合わせた構造化パイプラインでソースコードの脆弱性を自動発見する手法を公開し、防御側が攻撃者より先に脆弱性を特定できる体制を実現した。

AI SUMMARYGoogle Mandiant details an agentic vulnerability discovery framework that pairs AI models with expert-driven orchestration to find source code vulnerabilities faster than adversaries can exploit them after a data breach.

Staying Ahead of Adversarial AI Through Agentic Source Code Review
8/6(木)Thu, Aug 61 entries
🔥 HOT報道NewsNews/Policy·Ars Technica

欠陥のあるマザーボードコントローラを悪用して数千台のサーバにバックドアが仕掛けられる恐れThousands of servers can be backdoored by exploiting buggy motherboard controllers

重要度 HighHigh priority技術記事 · Industry & Policytechnical post · Industry & Policy

AI要約大手メーカー製のベースボード管理コントローラ(BMC)に深刻な脆弱性が発見され、攻撃者がサーバにバックドアを設置できる状態にあることが明らかになった。BMCはOS外で動作するため、侵害されると検出・除去が極めて困難になる。

AI SUMMARYSerious security flaws in baseboard management controllers from major manufacturers leave thousands of servers open to persistent backdoors. Because BMCs operate below the OS layer, successful exploitation is extremely difficult to detect or remediate.

Thousands of servers can be backdoored by exploiting buggy motherboard controllers
7/31(金)Fri, Jul 311 entries
🔥 HOT報道NewsNews/Policy·Ars Technica

Kremlinハッカーが最大深刻度のExchangeサーバー脆弱性を悪用中Max-severity Exchange server flaw under active exploitation by Kremlin hackers

重要度 HighHigh priority技術記事 · Industry & Policytechnical post · Industry & Policy

AI要約ロシア系ハッカーがMicrosoft Exchangeの最大深刻度の脆弱性を積極的に悪用しており、認証情報のローテーションやディスク再イメージ化後も持続するバックドアをサーバーに仕込むことが可能なため、未パッチ環境は早急な対応が必要。

AI SUMMARYRussian state-linked hackers are actively exploiting a maximum-severity Microsoft Exchange flaw to plant persistent backdoors that survive credential resets and disk re-imaging, making unpatched servers critically vulnerable.

Max-severity Exchange server flaw under active exploitation by Kremlin hackers
7/30(木)Thu, Jul 301 entries
報道NewsNews/Policy·Ars Technica

AnthropicはMicrosoftが修正できる速度を上回るペースでバグを発見しているAnthropic is finding bugs faster than Microsoft can fix them

重要度 MediumMedium priority技術記事 · Industry & Policytechnical post · Industry & Policy

AI要約AnthropicのAIがMicrosoftのソフトウェアの脆弱性を発見するペースが、Microsoftのパッチ適用速度を上回っており、ハッカーに先んじるための修正競争が激化している。

AI SUMMARYAnthropic's AI is uncovering Microsoft vulnerabilities faster than Microsoft's teams can patch them, raising urgent concerns about the widening gap between discovery and remediation.

Anthropic is finding bugs faster than Microsoft can fix them
7/24(金)Fri, Jul 241 entries
論文PaperPapers/Benchmarks·arXiv cs.SE

AIが生成したコードにおけるセキュリティ脆弱性パターン:モデル横断比較研究Security Vulnerability Patterns in AI-Generated Code: A Cross-Model Comparative Study

重要度 MediumMedium priority論文/研究 · Papers / Benchmarkspaper/research · Papers / Benchmarks

AI要約複数のAIコード生成モデルを横断的に比較し、生成コードに共通して現れるセキュリティ脆弱性のパターンを分析した研究。どのモデルがどの種類の脆弱性を生みやすいかを明らかにし、安全なAI活用に向けた知見を提供する。

AI SUMMARYThis study systematically compares security vulnerability patterns across multiple AI code generation models, identifying which weakness types each model tends to introduce. The findings offer actionable guidance for developers and organizations relying on AI-assisted coding.

Security Vulnerability Patterns in AI-Generated Code: A Cross-Model Comparative Study
7/22(水)Wed, Jul 221 entries
公式OfficialGemini/Gemma·Google Cloud Blog

プレビュー公開: CodeMender でソフトウェアの脆弱性を発見・修正Now in preview: Find and fix software vulnerabilities with CodeMender

重要度 MediumMedium priority技術記事 · Gemini / Gemmatechnical post · Gemini / Gemma

AI要約GoogleはAIを活用した脆弱性検出・修正ツール「CodeMender」をプレビュー公開した。開発者がセキュリティ問題を早期に特定し自動修正できる点が重要。

AI SUMMARYGoogle has launched CodeMender in preview, an AI-powered tool that helps developers automatically find and remediate software vulnerabilities, reducing security risk earlier in the development cycle.

Now in preview: Find and fix software vulnerabilities with CodeMender
7/21(火)Tue, Jul 212 entries
コミュニティCommunityCopilot·Qiita GitHub Copilot

OWASP Juice Shop で学ぶ Web 脆弱性 ― WSL 新CLI「wslc」で建てて、Defender / GitHub で裏取りするThis article demonstrates how to quickly spin up an OWASP Juice Shop…

重要度 MediumMedium priority技術記事 · GitHub Copilottechnical post · GitHub Copilot

AI要約WSL の新しいCLIツール「wslc」を使ってOWASP Juice Shopの学習環境を素早く立ち上げ、Microsoft DefenderとGitHubを活用してWeb脆弱性の理解を深める手法を解説した実践的な記事。

AI SUMMARYThis article demonstrates how to quickly spin up an OWASP Juice Shop environment using the new WSL CLI tool "wslc", then leverage Microsoft Defender and GitHub to validate and deepen understanding of common web vulnerabilities.

OWASP Juice Shop で学ぶ Web 脆弱性 ― WSL 新CLI「wslc」で建てて、Defender / GitHub で裏取りする
🔥 HOT報道NewsNews/Policy·TechCrunch

最近修正されたWordPressの脆弱性が悪用され、数百万サイトに危険Hackers are exploiting recently patched WordPress bugs, putting millions of websites at risk

重要度 HighHigh priority技術記事 · Industry & Policytechnical post · Industry & Policy

AI要約ハッカーが最近パッチされたWordPressの脆弱性を積極的に悪用しており、迅速に更新していないサイトが攻撃にさらされている。早急なアップデート適用が求められる。

AI SUMMARYAttackers are actively exploiting recently patched WordPress vulnerabilities, leaving unpatched sites exposed to compromise. Site owners are urged to apply updates immediately to reduce risk.

Hackers are exploiting recently patched WordPress bugs, putting millions of websites at risk
7/16(木)Thu, Jul 162 entries
🔥 HOT報道NewsNews/Policy·Ars Technica

Microsoft が史上最多パッチをリリースした当日に Windows のゼロデイ脆弱性が公開されるWindows 0-day drops the same day Microsoft releases record number of patches

重要度 HighHigh priority技術記事 · Industry & Policytechnical post · Industry & Policy

AI要約Microsoftが過去最多規模のパッチチューズデーを展開した同日、Windows のゼロデイ脆弱性が公開され、修正前に悪用されるリスクが高まっている。

AI SUMMARYA Windows zero-day vulnerability was publicly disclosed on the same day Microsoft issued a record-breaking Patch Tuesday, raising urgent concerns about active exploitation before users can apply fixes.

Windows 0-day drops the same day Microsoft releases record number of patches
🔥 HOT報道NewsNews/Policy·TechCrunch

MicrosoftがAI活用により過去最多のセキュリティ脆弱性を修正Microsoft patches record number of security vulnerabilities, citing its use of AI

重要度 HighHigh priority技術記事 · Industry & Policytechnical post · Industry & Policy

AI要約MicrosoftはAIを活用することで記録的な数の脆弱性を発見・修正したと発表した。AIがセキュリティ対応の規模と速度を大幅に向上させた点が注目される。

AI SUMMARYMicrosoft disclosed a record-breaking number of patched security vulnerabilities, crediting AI-assisted tools for accelerating discovery and remediation at unprecedented scale.